The Price of Commoditization
The conversation about commoditization in professional services usually stays at the pricing and positioning level. When you compete on price, you attract price-sensitive clients who leave the moment a cheaper option appears. Competing on price is a race to the bottom that no one wins sustainably, and the strategic argument against it is both correct and well-established. But it is also insufficient as a complete account of what commoditization actually costs — because it frames the problem as a strategic mistake about market positioning when the more significant and more consequential damage from commoditization pressure operates at a deeper level, inside the actual delivery of the service itself.
The real cost of competing on price in a service business is not primarily what it does to your client mix or your margin profile, significant as both are. Those are real and they matter. But the most consequential damage from sustained commoditization pressure happens inside the service itself: in the decisions that get made about how the work is staffed, how thoroughly it is done, what corners can be rounded and what investments are deferred, and — most consequentially in security and IT — in what kinds of capabilities the organization is able to maintain when every budget conversation is anchored by what the lowest-cost provider charges for a nominally similar set of services.
Price competition produces service delivery compromises. That is the argument that does not get made clearly enough, and it is the one that matters most for clients trying to evaluate what they are actually buying when they evaluate providers.
The Staffing Equation
The most direct and immediate consequence of commoditization pressure on service delivery is in staffing. Every managed service has a cost structure, and the largest component of that cost structure is people. When pricing is driven down by competition, something in the cost structure has to give, and in a people-intensive service business, the primary lever is almost always headcount: fewer people per client, less experienced people, higher turnover, or some combination of all three.
This is not a failure of ethics or integrity. It is arithmetic. An organization that has priced itself at the level required to win in a commoditized market cannot staff at the level required to deliver a genuinely high-quality service, because the revenue per client does not support the labor cost per client that the service actually requires. The math does not work out, and the gap gets closed somewhere.
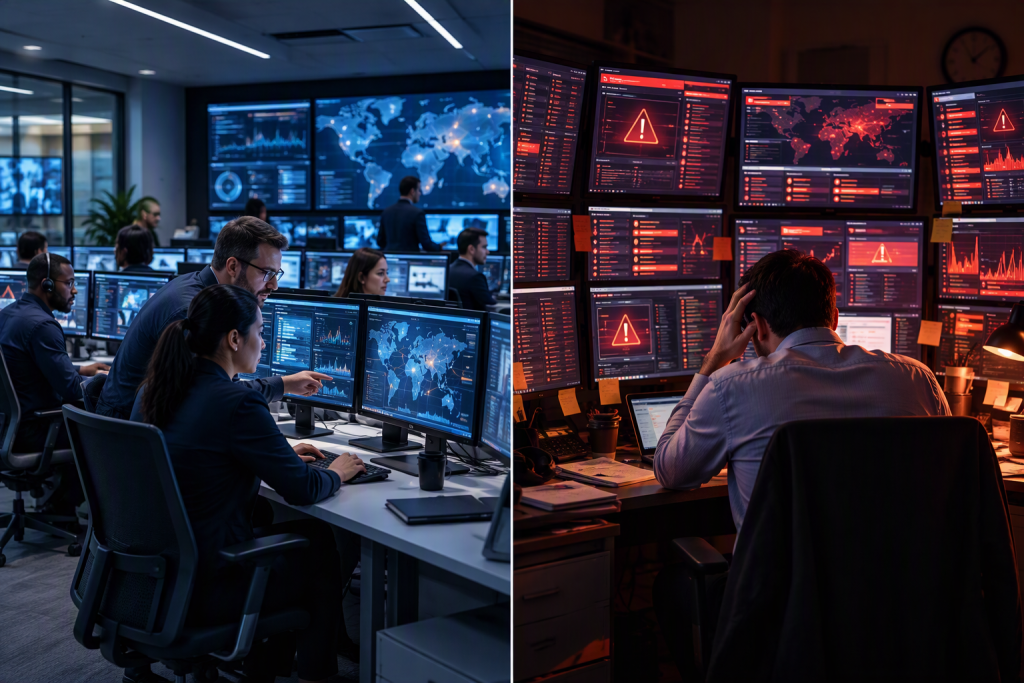
In managed IT and security services, where it gets closed matters enormously. The provider who is managing eight hundred endpoints per analyst rather than three hundred is a provider whose analysts are spending their time in reactive mode — responding to alerts and handling tickets — rather than in the proactive monitoring, threat intelligence review, and vulnerability assessment work that determines whether the security program is actually functioning or just generating the appearance of functioning. The client is receiving the outputs that the contract specifies: monitoring coverage, response times, compliance reporting. What the client is not receiving is the depth of engagement and the proactive attention — the continuous monitoring of the threat intelligence, the vulnerability assessment work that runs on its own schedule rather than being triggered by incidents, the proactive program reviews that would surface gaps before they become exposures — that the service was supposed to provide and that the staffing model no longer supports.
The client rarely discovers this until they need it. The security program that appears to be working at the commoditized price point looks exactly like the security program that is working. The gap between the two becomes visible when something goes wrong that adequate coverage would have caught, or when a compliance review surfaces that the program being maintained is a documentation program rather than a security program.
The Technical Debt That Commoditization Builds
The staffing consequences of commoditization are the most visible expression of a broader pattern: when pricing pressure is severe enough, it forces providers to defer the investments that are not immediately visible to clients but that determine the long-term quality of what the client is receiving.
Security tooling and infrastructure require investment to stay current. The threat landscape evolves continuously, and the tools that provided adequate coverage eighteen months ago may not provide adequate coverage today. An organization under severe pricing pressure defers these investments — not because it does not understand their importance, but because the revenue does not support the capital outlay required to stay current. The client is protected by the security stack that was current when the engagement began, which is increasingly less adequate with every quarter that passes without reinvestment.
Training and development face the same pressure. The security analyst whose skills are current with how actual threat actors are operating today is more expensive than the analyst whose skills were current two years ago. The organization that cannot invest in continuous development of its people because the pricing model does not support that investment is an organization whose delivery capability quietly degrades over time. The people are the same. The work looks the same. The actual protection they are able to provide is materially less than it was, because the knowledge and techniques required to provide real protection are not static and the investment in keeping them current has not been made.
Documentation, process improvement, and program development — the internal work that turns reactive security activity into a structured, continuously improving security program — require time and attention that a commoditized staffing model simply does not leave room for. The result is a security program that is perpetually in execution mode and never in improvement mode. Each client gets what the previous engagement produced. The program does not develop, because development requires protected time that the economics do not support.
What the Client Is Actually Evaluating
The challenge for clients evaluating security and IT providers is that the consequences of these delivery compromises are mostly not visible at the time the buying decision is made. The provider who wins on price presents a set of capabilities that appears equivalent to the provider who costs more. The contract covers the same categories of service. The sales process emphasizes the same outcomes. The reference calls are from clients who have not yet had the significant incident that would surface the gap between what the contract promises and what the delivery model actually supports.
The due diligence that would reveal the difference requires asking different questions than the ones that typically appear in a technology vendor evaluation. Not “do you provide 24/7 monitoring” but “what is your analyst-to-endpoint ratio and how has it changed in the last two years.” Not “do you handle compliance reporting” but “walk me through the last compliance program you built from scratch and describe what was involved.” Not “what is your response time SLA” but “describe your last significant incident response engagement and what your team’s decision process looked like under pressure.”
These questions do not appear in most technology vendor RFPs because the people writing them have not been through a significant security incident and do not know what adequate versus inadequate response looks like from the inside. The clients who learn to ask them are the ones who have usually learned the hard way — after an incident that revealed that the coverage they were paying for was not the coverage they were receiving.
The Integrity of the Service
There is a line in managed security and IT services where the price compression has become severe enough that the service is no longer the service. The monitoring is happening, but the analysts are not engaged at the depth required to catch what matters. The compliance program is being maintained, but it is a documentation program rather than a living security posture. The infrastructure is being managed, but the proactive work that prevents the crisis five years from now is not being done because the staffing model does not support it.
This is not a theoretical risk. It is a specific and predictable outcome of pricing dynamics that force delivery compromises, and it affects clients who never asked for a compromised service and do not know they are receiving one.
The organizations that avoid it are the ones that have learned to evaluate what they are buying at the service delivery level rather than the contractual level — to understand that the price they are paying determines the economics that the provider operates under, and that those economics determine what the provider can and cannot do in the actual delivery of the service. Choosing the lowest price in security services is not saving money on a commodity the way you might negotiate a lower rate on office supplies. It is accepting a reduced level of actual protection while paying for the appearance of full coverage — and the difference between those two things is what determines whether the organization is actually protected or just believes it is.
The Regulatory Consequence
In healthcare and accounting, the delivery compromises produced by commoditization pressure carry a specific additional cost that is worth naming explicitly: regulatory exposure that the client does not know they are carrying.
HIPAA’s security requirements and the FTC Safeguard Rule both impose substantive obligations on the organizations they govern. The security program required to actually meet these obligations is not a documentation exercise — it is a functioning program with a designated owner, documented and tested controls, regular risk assessments conducted with genuine depth, and incident response procedures that have been practiced rather than filed. Building and maintaining this program requires the kind of sustained attention and expertise that a commoditized security provider, operating under the staffing and investment constraints that the pricing model requires, is structurally not able to provide.
The client who believes they are receiving compliant security services because they have a managed security contract and a compliance report does not know whether the program being maintained is the program the regulation requires. The compliance report reflects what the provider documented. It does not reflect whether the controls are actually functioning, whether the risk assessment was conducted with the depth and independence the regulation expects, or whether the incident response plan has ever been tested against a realistic scenario. These are differences that become visible to regulators during an enforcement action and to the organization during a breach response — and in both cases, the visibility comes too late to avoid the consequences.
The organizations that have navigated regulatory scrutiny after a security incident with their compliance posture intact tend to have one thing in common: they invested in a security program that was built to actually work, not to produce documentation at the lowest possible cost. The pricing they paid supported the staffing and investment required to do the work. The compliance program they maintained was a security program that happened to generate compliant documentation, not a documentation program that asserted security.
The Selection Effect
There is a self-reinforcing dynamic in commoditized markets that is worth understanding because it operates against clients’ interests in ways they do not always anticipate.
When pricing in a market is driven to a level that requires delivery compromises, the providers who survive and grow in that market are the ones who have become most efficient at making those compromises without losing the contract. They have optimized the appearance of the service — the metrics, the reports, the language of the sales process — while reducing the substance. The providers who have maintained higher standards at higher prices either exit the market, reposition to a different segment, or struggle to compete for clients who are evaluating primarily on price.
The result, over time, is that the clients who buy on price are selecting disproportionately from the providers who have optimized for appearing to provide the service rather than actually providing it. This is not a moral judgment about those providers. It is the predictable outcome of a market dynamic that rewards the appearance of value over its substance — because in a commoditized market, appearance and substance look the same right up until the moment they do not.
The clients who eventually learn to evaluate security and IT providers at the service delivery level — who ask the questions about staffing ratios, about investment in tooling and development, about what the actual program looks like underneath the contract — are the clients who tend to find that the premium they are paying for a provider who has maintained delivery standards is considerably smaller than the risk they were accepting by paying the lowest available price.
What Good Looks Like
The alternative to commoditized security services is not just more expensive security services. It is a different relationship with what security is and what it is supposed to do.
A security program that is working is not generating monitoring outputs and compliance reports. It is actively maintaining a current, accurate understanding of the organization’s actual risk posture — where the real exposures are, how they have changed since the last assessment, what the highest-priority actions are, and whether the controls in place are functioning as assumed. It is producing that picture for leadership and the board at a level of specificity and honesty that allows them to make informed risk decisions. It is developing the people and the program continuously, so that the coverage the client has today is better than the coverage they had a year ago.
This is what the contract is supposed to deliver. Whether the economics support actually delivering it is a question that the price determines, and it is a question clients are better served by asking explicitly before the gap between promise and delivery becomes apparent in the worst possible circumstances.
Tom Glover is Chief Revenue Officer at Responsive Technology Partners, specializing in cybersecurity and risk management. With over 35 years of experience helping organizations navigate the complex intersection of technology and risk, Tom provides practical insights for business leaders facing today’s security challenges.
Eliminate All IT Worries Today!
Do you feel unsafe with your current security system? Are you spending way too much money on business technology? Set up a free 10-minute call today to discuss solutions for your business.